Calendar sharing used to be treated as a simple convenience: give a colleague access, let a vendor check your schedule, and move on.
That approach no longer fits how companies work.
Today, employees coordinate with vendors, clients, contractors, consultants, and partner organizations across different systems. A calendar may contain much more than meeting times. Titles can reveal strategic initiatives. Locations can expose offices or customer sites. Attendee lists can identify clients, investors, or legal advisers. Descriptions may contain confidential notes.
That is why organizations are rethinking free busy calendar sharing, external participant calendar availability, and the role of shared calendar software in 2026.
The practical goal is straightforward:
Share enough availability to coordinate efficiently: but no more information than the task requires.
Calendar access should match the job
The principle behind a better calendar policy is least privilege.
The National Institute of Standards and Technology (NIST) defines least privilege as restricting access to the minimum necessary to accomplish an assigned task. NIST’s SP 800-53 AC-6 control applies that principle to users, processes, and system access.
For calendar sharing, that means asking one question before granting permission:
What does this person actually need to see or do?
A vendor coordinating a project may need to know when your team is available. They probably do not need to see the title of an internal planning session.
An executive assistant may need to edit certain events. They may not need unrestricted access to private appointments or the ability to change sharing settings.
A former contractor may need no access at all.
The permission should follow the task: not the other way around.
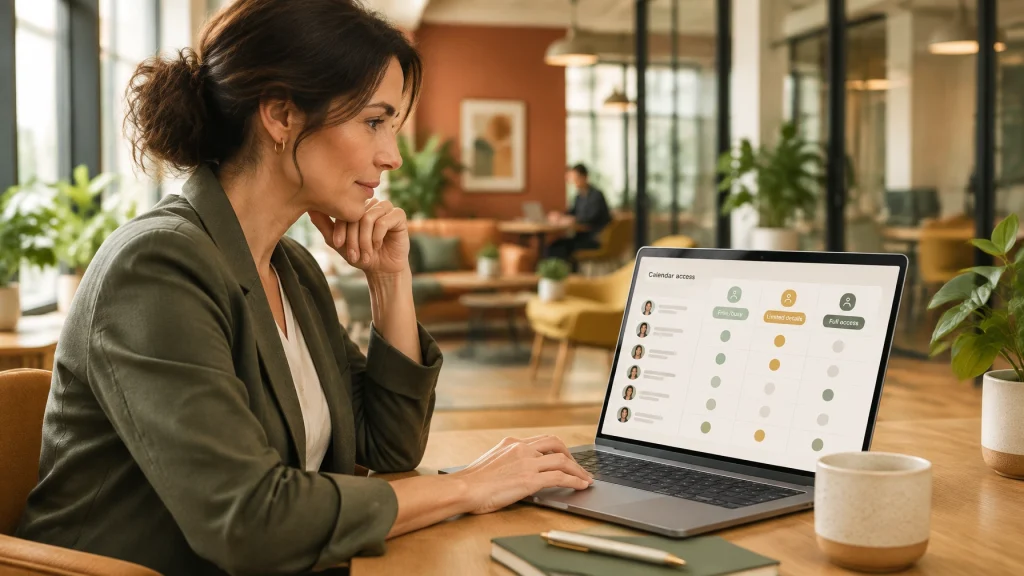
The four calendar-sharing levels to understand
Most calendar platforms provide several access tiers. The names differ between Google Calendar and Outlook, but the basic model is similar.

1. No access
The person cannot view your calendar or query your availability.
Use this level when:
- The relationship does not require scheduling visibility.
- A project has ended.
- A vendor is no longer active.
- A user has changed roles.
- An external organization should not receive availability information.
No access is the cleanest option when there is no legitimate scheduling need.
2. Free/busy only
This is usually the best default for external collaborators.
Google describes its option as “See only free/busy (hide details).” The equivalent Microsoft Outlook permission is commonly presented as “Can view when I’m busy.”
At this level, the recipient can see whether a time is available or blocked. They cannot see event titles, descriptions, locations, guests, or notes.
The Google Calendar sharing documentation and Google Calendar API sharing model both distinguish free/busy access from event-detail access.
Microsoft uses similar distinctions. Its external calendar-sharing guidance includes a “free/busy information with time only” option, while Exchange organization relationships can use the AvailabilityOnly level.
This level supports external participant calendar availability without exposing the context behind each appointment.
3. Limited details
Limited access may reveal event titles and locations while hiding descriptions, notes, or attendee information.
This can be useful internally when a team needs context to coordinate work. It is more sensitive when used with clients, vendors, or other external collaborators.
A title such as “Customer contract review” or “Acquisition planning” may look harmless. It can still reveal business priorities, relationships, or confidential activity.
Treat limited details as a meaningful data disclosure: not as a minor step above free/busy.
4. Full details, editing, or delegation
Full read access may expose titles, locations, descriptions, attachments, and attendee lists. Editing access adds the ability to create, change, or delete events.
Delegation and calendar-management permissions can go further by allowing someone to manage sharing or act on another person’s behalf.
These permissions may be appropriate for a small number of trusted roles. They should not be the default for a broad team, an external vendor network, or a multi-company meeting scheduling process.
Metadata deserves the same attention as meeting content
Organizations often protect documents and email while overlooking calendar metadata.
That is a mistake.
Calendar metadata can include:
- Client and prospect names.
- Office or project locations.
- Internal initiative names.
- Legal or personnel-related meeting titles.
- Attendee relationships.
- Travel patterns.
- Recurring executive meetings.
- Vendor and partnership activity.
A person does not need to read meeting notes to learn something sensitive. A calendar title and attendee list may be enough.
The 2025 Verizon Data Breach Investigations Report analyzed 22,052 security incidents and 12,195 confirmed breaches. Verizon reported that the human element appeared in about 60% of breaches, while credential abuse represented 22% of breach initial-access vectors.
These figures are not calendar-specific, and they do not prove that calendar sharing caused those incidents. They do show why access decisions should account for ordinary human error, compromised accounts, and unnecessary permissions.
The exposure may begin with a well-intentioned share that remains active long after the original purpose ends.
External sharing needs an organization-wide policy
Individual users should not be expected to make every access decision without guidance.
A practical calendar policy should define:
-
Default external access
Set free/busy only as the standard for external organizations unless a documented business need requires more. -
Approved exceptions
Define when limited details, editing, or delegation may be granted. -
Data restrictions
Prohibit confidential information, credentials, sensitive customer details, or unnecessary personal information in event titles and descriptions. -
Administrative controls
Configure Google Workspace or Microsoft 365 settings to prevent users from exceeding the organization’s approved external-sharing level. -
Review ownership
Assign responsibility for reviewing calendar permissions rather than assuming each user will remember. -
Offboarding requirements
Include shared calendars, delegated access, group permissions, and third-party scheduling tools in departure checklists.
Policy creates consistency. It also reduces the chance that one overly broad permission undermines a carefully managed security program.
Review calendar permissions on a regular schedule
Access should not be permanent simply because it was once useful.
NIST’s access-control guidance includes periodic review of user privileges and the removal or reassignment of privileges that are no longer needed. A calendar permission review can be simple:
- Review external shares at least quarterly.
- Review access after a project ends.
- Review permissions when someone changes roles.
- Remove vendor access when a contract closes.
- Confirm that delegates still support the same executive or team.
- Check for group-based access that may be broader than expected.
- Remove duplicate or abandoned calendar integrations.
Offboarding deserves special attention. Disabling a user account may not remove every permission they received elsewhere. A departing employee may still appear in a shared-calendar group, delegated calendar list, or third-party scheduling workspace.
A complete offboarding review should answer:
Who can still see this calendar, and what exactly can they do?
Choose scheduling tools that minimize exposure
Traditional calendar sharing often forces companies to choose between two imperfect options:
- Share too much calendar information.
- Spend time exchanging availability manually.
Modern tools should separate those concerns.
A privacy-first calendar scheduling tool or meeting scheduler app should help people find overlapping availability without requiring full calendar access. That is especially important for cross-company scheduling, cross organization calendar coordination, and teams that need to coordinate calendars across companies.
CalendarConnect is designed for this narrower use case. Each participant authorizes access once, and the platform identifies mutual free/busy availability across Google and Outlook calendars. It does not require calendar migration, and participants do not expose event titles, notes, locations, or attendee lists.
The result is a free busy calendar across organizations that supports external coordination without turning every calendar into an open book.
CalendarConnect only identifies mutual free/busy availability. It does not automatically send invitations, book meetings, or create calendar events. After selecting a suitable time, you continue using your existing calendar workflow to arrange the meeting.
That distinction matters. The tool helps answer “When can everyone meet?” without taking control of what happens next.

A practical permission checklist for 2026
Before granting calendar access, use this short review:
Define the purpose
Write down why the person or organization needs access.
“Schedule a project call” is specific. “General visibility” is not.
Select the lowest useful permission
Start with no access. Move to free/busy only if availability is required. Grant limited details or editing only when the task cannot be completed otherwise.
Limit the audience
Share with named individuals or approved groups instead of broad public or organization-wide access whenever possible.
Protect event metadata
Use neutral titles for sensitive appointments. Do not place confidential notes or unnecessary personal information in calendar fields.
Set an expiration or review date
If the system supports expiration, use it. If not, record a review date in your access process.
Recheck after changes
Review permissions after projects, contracts, reporting lines, or executive-assistant assignments change.

Better sharing creates better coordination
Calendar privacy and scheduling efficiency do not have to compete.
A well-governed shared calendar software strategy gives employees the visibility they need while protecting confidential details. Free/busy sharing is often enough for external clients, vendors, partners, and consultants. More detailed access should be the exception, supported by a clear business reason.
The broader security context reinforces the value of restraint. IBM’s 2025 Cost of a Data Breach Report places the global average cost of a data breach at $4.44 million. That number is not a reason to treat every calendar as a critical security system. It is a reminder that small access decisions should be made deliberately, especially when they affect external relationships.
For teams looking to schedule meetings with external clients, compare external availability across organizations, or use an Outlook Google Calendar availability checker without exposing event details, the right approach is clear:
Share availability. Protect context. Review access. Remove permissions when the need ends.
Explore CalendarConnect to see how privacy-first multi-company meeting scheduling can support your existing workflow without migration.
Ready to simplify how your team schedules across organizations? Try CalendarConnect free at calendarconnect.net